In brief
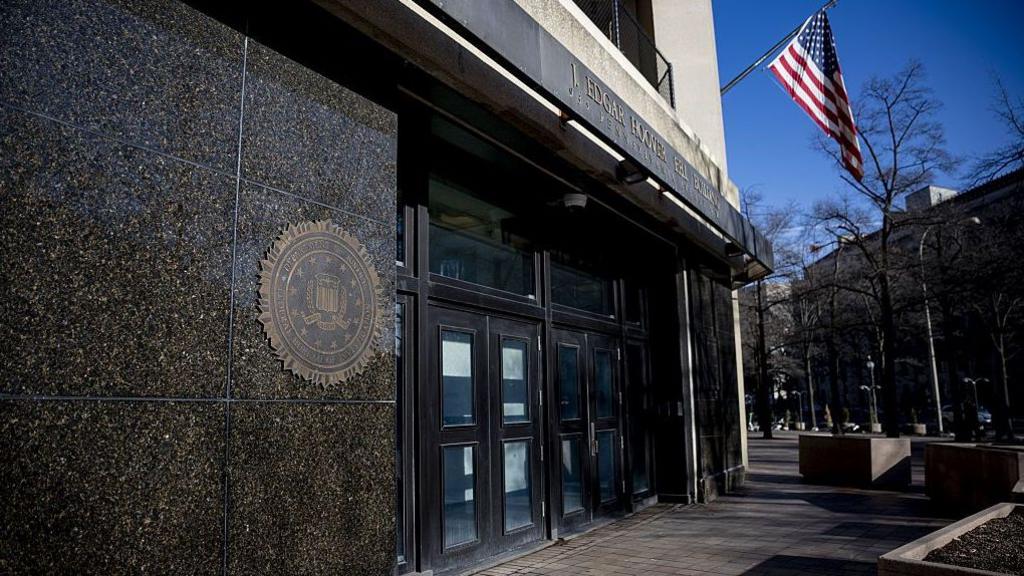
ShinyHunters, a notorious cyber‑criminal collective, has breached the FBI’s systems, leaking contact details, addresses, and medical records of every agent. The agency now faces threats to publish the data unless it retracts a 2023 advisory, igniting outrage and intense scrutiny over internal security practices. Agents fear targeted attacks and personal risks, while the FBI vows to cooperate with other agencies to hunt the hackers. The incident marks a rare breach of a top‑tier U.S. law‑enforcement agency, raising alarms about national security and the safety of officers' families.
Immediately after a security breach by the hacker collective ShinyHunters was confirmed, FBI staff across the agency voiced shock and outrage. The attack exposed private data for every agent, from home addresses and phone numbers to medical records and confidential badge details.
“Our undercover work is at risk,” said one former agent who wishes to remain anonymous. “If criminals can read our personal emails, they can locate our families.”
ShinyHunters, known for high‑profile extortion schemes, is demanding the FBI retract a public advisory issued earlier this year. Their threat is not for money but to publish the database on the dark web unless the agency complies.
The group could leverage the exposed information to launch “violence‑as‑a‑service” phishing and intimidation campaigns against former or current officers.
In response, the FBI has opened a multi‑agency investigation, warning that it will “make this group suffer the consequences.” Experts say the breach exposes sloppy security practices, leaving a wide window for hostile nation‑states to target agents.
For the first time, profile data in the public domain could fuel targeted harassment and recruitment efforts, putting both agents and their families at unprecedented risk.
PulseWire urges any witness to the hack or its fallout to report immediately to law‑enforcement channels and to verify information through official statements to help keep the community safe.